
- Blockchain investigator ZachXBT says individuals linked to the laundering of funds from the $387.5 million Bitget security breach are openly seeking help through Discord and Telegram channels used by crypto services.
Blockchain investigator ZachXBT said Monday that people allegedly involved in moving funds stolen in the $387.5 million Bitget hack are using public Discord servers and Telegram channels to seek assistance with transactions.
The claims came four days after Bitget disclosed unauthorized transfers from part of its hot and warm wallet infrastructure. The exchange later revised its estimate of affected assets from $351.6 million to approximately $387.5 million after identifying additional transactions involving Zcash and TRON.
In a post on X, ZachXBT said the actors were allegedly laundering funds on behalf of attackers suspected of being linked to North Korea. He said the individuals were openly asking for assistance with orders through public channels operated by services they were using to move the stolen assets.
The investigator also published screenshots and transaction data connecting several aliases with wallets associated with the Bitget breach.
Bitget Funds Moving Across Multiple Networks
ZachXBT said the stolen assets are being moved between blockchains through cross-chain bridges and subsequently into services designed to make transaction tracing more difficult. One of the aliases identified in the investigation, referred to as “Alias 4,” was also linked by ZachXBT to the laundering of funds from the $292 million Kelp DAO exploit in April.
The Kelp DAO attack involved the theft of approximately 116,500 rsETH from a LayerZero-powered bridge. A subsequent LayerZero incident report said Mandiant, CrowdStrike, and independent security researchers attributed the attack to the North Korean threat actor known as TraderTraitor, also referred to as UNC4899.
Chainalysis separately found that attackers had compromised off-chain infrastructure connected to the Kelp DAO bridge and manipulated data used by the bridge's verification system.
ZachXBT said the current movement of Bitget funds shows similarities to laundering patterns observed after other exploits attributed to TraderTraitor. The screenshots published alongside his post show users communicating with operators of crypto services about transactions that had become delayed or failed.
One account identified as “Cc” reportedly said that 277,724 XRP had been sent but only 431 XRP was returned. Another account, identified as “jack,” also appeared in the screenshots. ZachXBT connected the accounts to transaction activity associated with the stolen Bitget funds.
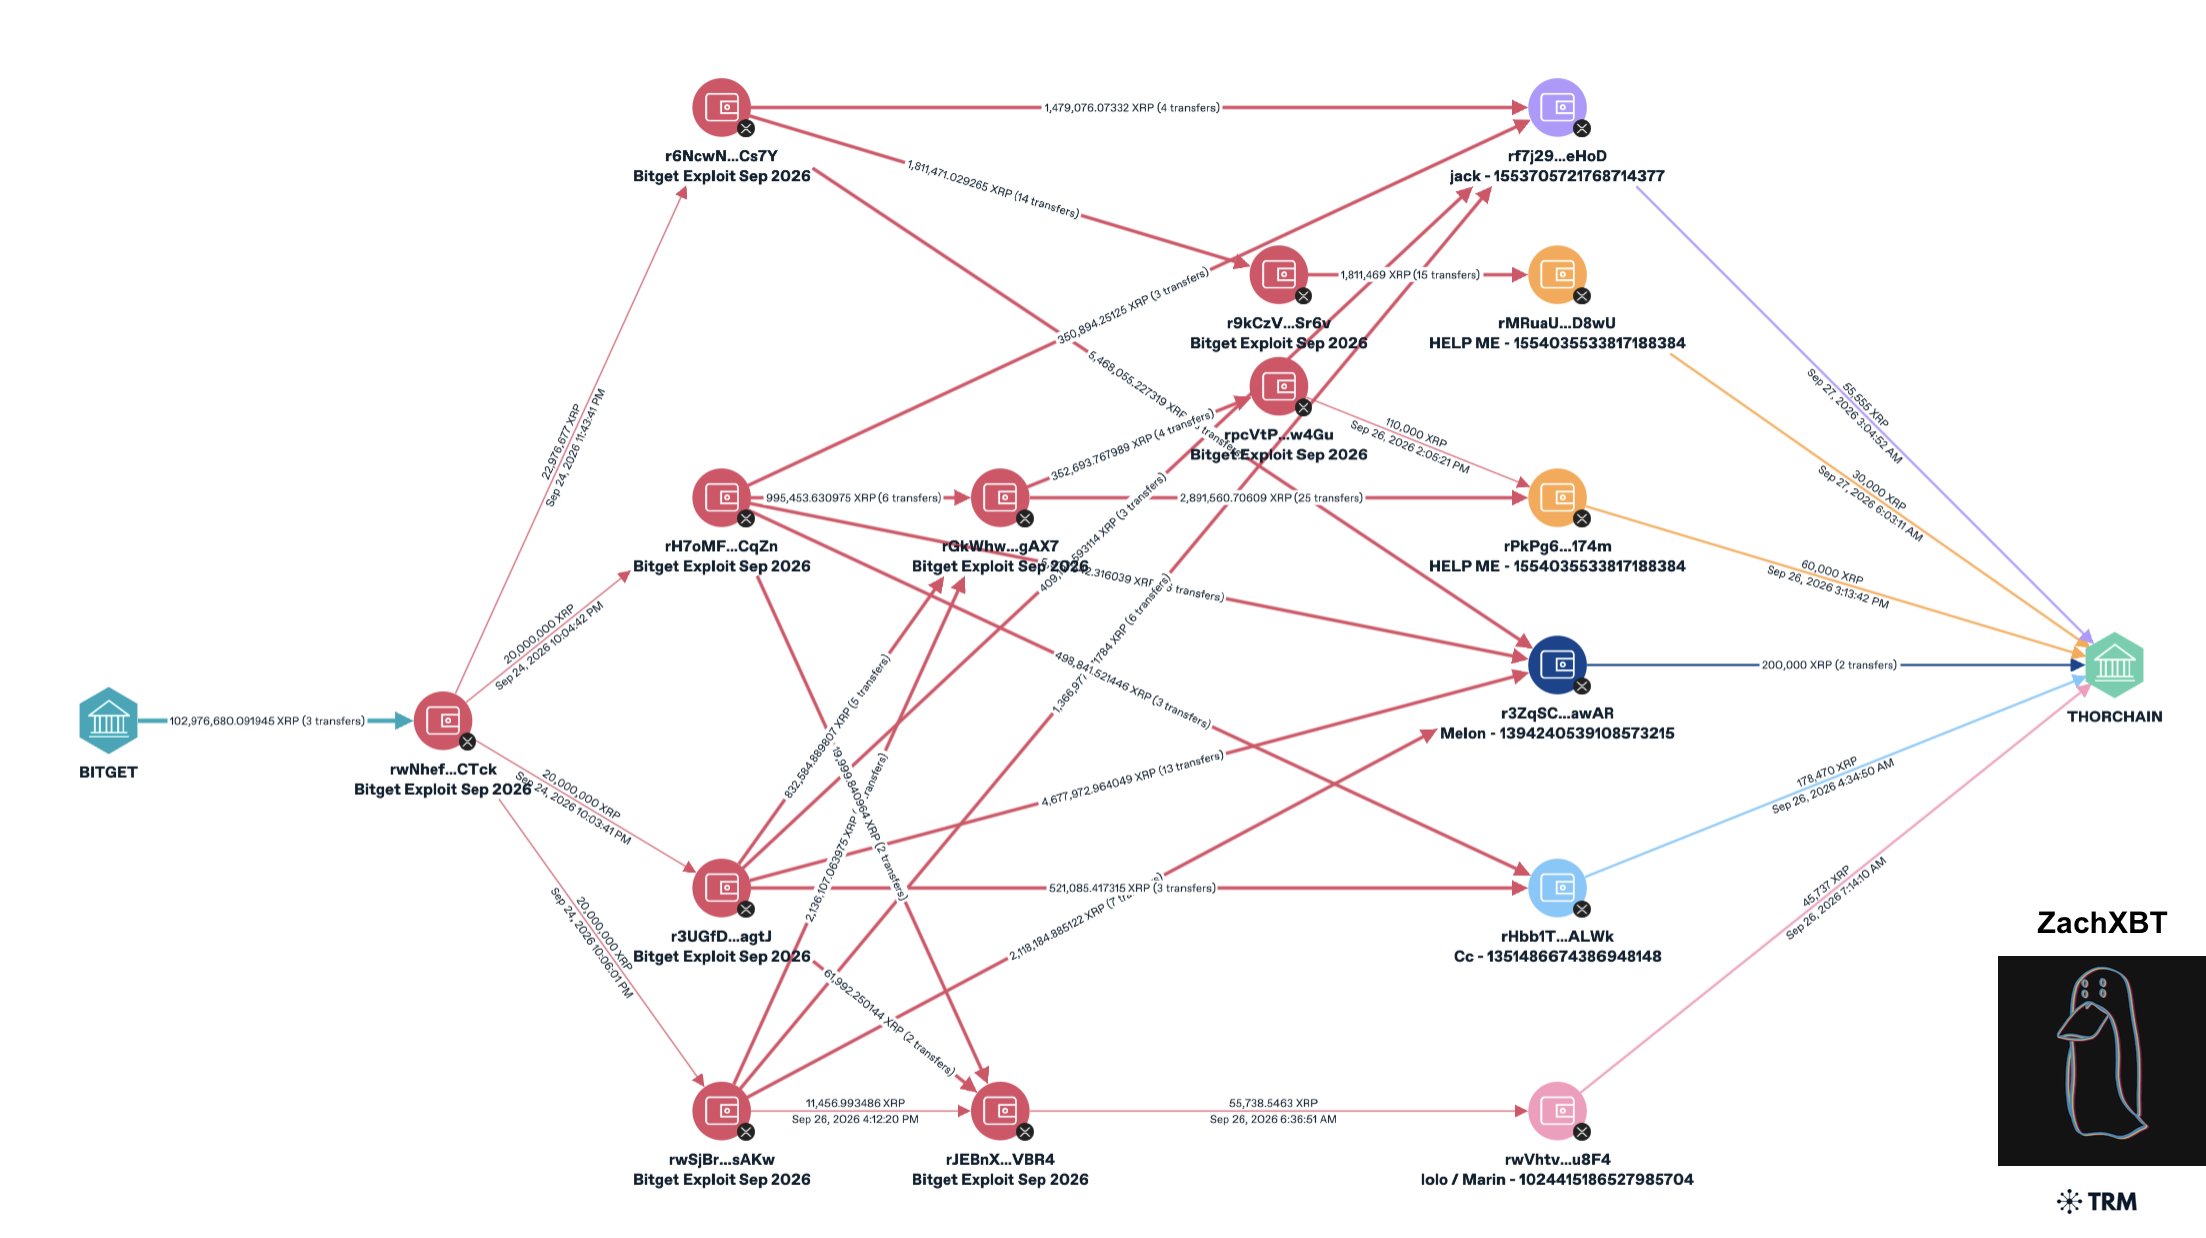
The public complaints provide on-chain investigators with additional information because transaction hashes, wallet addresses, and service interactions can create links between pseudonymous accounts and previously identified blockchain activity.
That does not establish the legal identity of the people behind the aliases. But ZachXBT said he expects to release more information about the groups involved in the coming weeks.
Bitget Investigation Remains Ongoing
Bitget said it identified and remediated the underlying vulnerability behind the incident and that the breach had been contained. Bitget said the breach affected assets across Ethereum and several other networks, including the XRP Ledger, Zcash and TRON. Its revised $387.5 million estimate included affected assets that were not included in the exchange's original calculation.
The exchange also said its cold wallets were not affected and that no further unauthorized transfers had been identified after containment. The company said its User Protection Fund held more than $464 million at the time of the incident.
The crypto exchange said it has been working with Mandiant and SlowMist on its investigation and fund-recovery efforts. Bitget also launched a recovery bounty program as investigators traced the stolen assets across multiple networks.
The latest developments add another layer to the investigation because the movement of funds after a hack can determine how much of the stolen value remains identifiable or potentially recoverable.